


Hi,
I created a policy to automatically enroll mail OTP when:
Users are created via: OPERATION.operation == ObjectOperation.CREATE
Users update their email address via OPERATION.operation == ObjectOperation.PATCH && CHANGES.hasAttributeChanged("email")
A flag is then applied and a policy runs to enroll users with said flag.
The script is working as intended for creations, however it does not seem to detect when the identity is patched:
The Identity Patch is VISIBLE in the user audit:
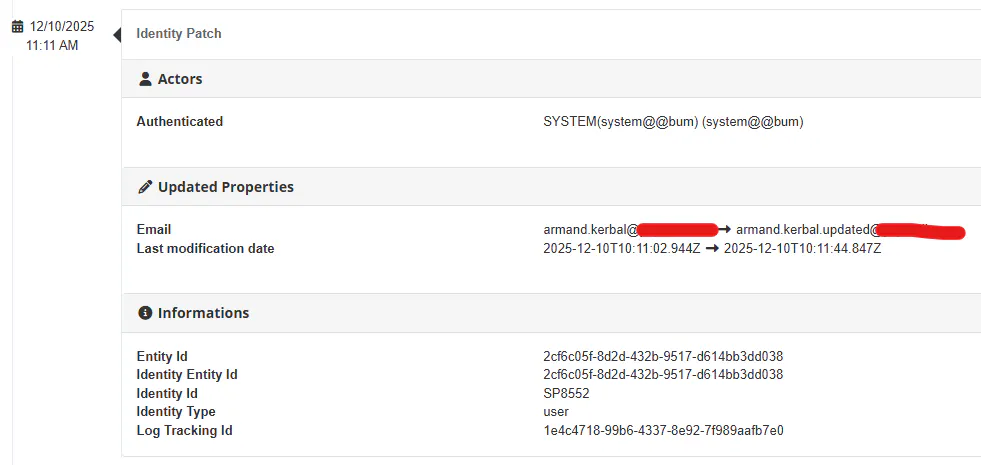
However, the user does not get the flag and therefore is not enrolled.
The stage is COMMON_PRE
What am I missing? Below the full script.
<script><![CDATA[

                import com.memority.citadel.shared.api.im.Flag
                import com.memority.citadel.shared.api.im.operation.ObjectOperationOptions
                import com.memority.toolkit.rule.api.ActionOutcome

                // This policy add a flag on new user. This flag will launch a business policy that will give an otp mail right grant

                LOG.debug("identity-user-creation-lifeCyclePolicy - object id {} ", OBJECT.id)

                if (OPERATION.operation == ObjectOperation.CREATE || (OPERATION.operation == ObjectOperation.PATCH && CHANGES.hasAttributeChanged("email"))) {
                    if(OBJECT.flags){
                        OBJECT.flags.add(Flag.F01)
                    } else {
                        OBJECT.flags = [Flag.F01]
                    }
                }
]]></script>Hi,
Turns out the policy was actually deactivated by default. It had been reactivated manually but delivering the tenant would deactivate it.
The policy is working as intended now.

